Security & trust
Your leads are your business. We treat them that way.
Who can see what is decided by roles you control. Every change is recorded. Data travels encrypted. And we tell you plainly what we do and don't hold certificates for.
Access
Least access by default.
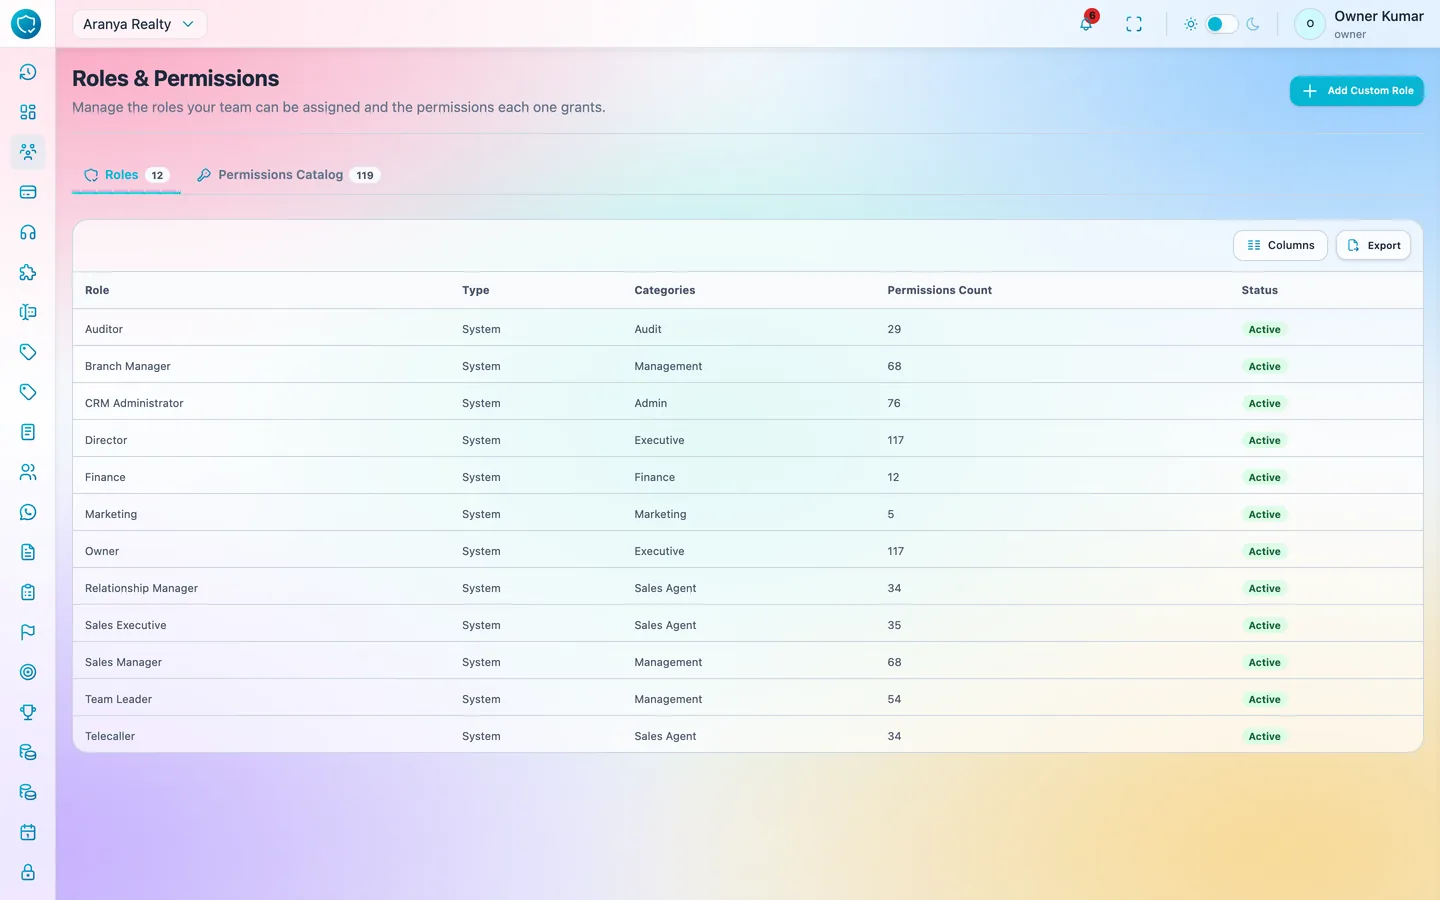
A salesperson sees only the leads assigned to them. Managers see their teams. Owners and directors see everything. Twelve roles ship ready, and about 110 action-level permissions let you shape custom ones, down to who may export, reassign or change a discount.
- Agents see only their own leads. Visibility follows assignment and the org chart.
- Exports are a permission, not a given. Decide who can take data out.
- Discount limits per user, with an approval ladder above them.
Accountability
Everything leaves a trail.
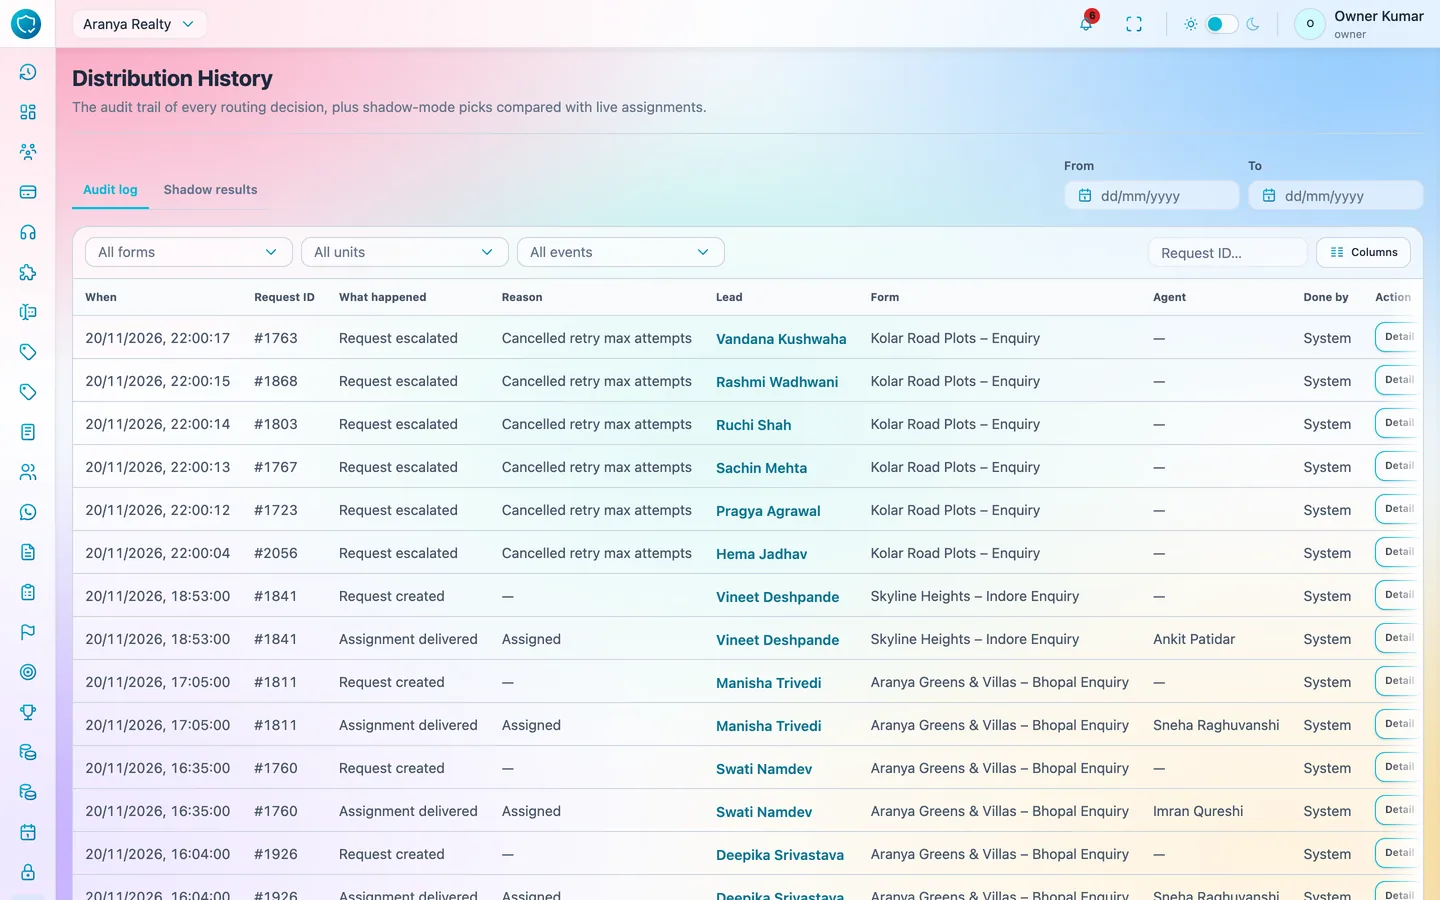
The audit log records who changed what and when, across settings, users, roles and records. Every routing decision is kept with its reason. Outcomes can only be logged against calls that actually happened.
- Audit log of changes to settings, users and roles.
- Distribution history for every assignment and escalation.
- API keys per system, revocable at any time.
Infrastructure
The basics, done properly.
Encrypted in transit
Every connection to the web app, the Android app and the API uses HTTPS (TLS).
Dedicated sign-in service
Sign-in runs on a separate identity service, so passwords never touch the CRM's own database.
Workspace isolation
Each company's data lives in its own workspace and is scoped on every request.
Secured cloud hosting
Hosted on secured cloud infrastructure with restricted, logged administrative access.
Backups
Databases are backed up on a schedule, and backups are access-restricted.
Seat-based write access
A user without a seat can view but not change anything, which limits who can alter data.
Law & compliance
Built around Indian data-protection law.
For the leads and customers you manage in CustomerBond, your business is the Data Fiduciary under the Digital Personal Data Protection Act, 2023, and Govindani Infotech acts as your Data Processor, under a written Data Processing Addendum. Consent and do-not-disturb preferences are recorded per person and respected on every WhatsApp send.
We report cybersecurity incidents to CERT-In as Indian law requires, and we will tell affected customers without undue delay.
What we don't claim: we do not currently hold ISO 27001 or SOC 2 certification. If your procurement team needs a security questionnaire answered, we're happy to do that.
Found a vulnerability?
Please tell us privately before telling anyone else. The responsible disclosure section of our Security Policy says how.
Stop losing the leads you already paid for.
See CustomerBond on your own lead sources, with your own team structure, in a 30-minute walkthrough.